How to patch your servers against nginx2root
A critical nginx flaw lets a stranger run commands on your server. Here is how to close it, and the automation I prepared in Unolia to do it for you.
nginx2root is a set of five nginx vulnerabilities, fixed on 18 November. The worst one sits in the HTTP/2 code and lets an unauthenticated visitor run commands on the server. Chained with a separate Linux kernel bug, it ends with root. Every nginx since 1.9.5 without the fix and with HTTP/2 enabled is exposed, which is most of them.
Here is how to handle it.
- Upgrade nginx to 1.31.9 (mainline) or 1.30.7 (stable), or install your distribution's security update. Distributions backport fixes without changing the version number, so check the package against its advisory rather than trusting
nginx -v. - Restart, do not reload.
nginx -s reloadkeeps the old binary running. Restart the service and check that no old worker is left. - Cannot upgrade today? Turn HTTP/2 off on every listener (
http2 offfrom nginx 1.25.1, or drophttp2from thelistenline before that), runnginx -t, reload withnginx -s reload, then check from outside that the server no longer negotiates h2. This only covers the HTTP/2 flaws, not the other CVEs, so upgrade as soon as you can. - Patch the kernel when your vendor ships its fix. Upgrading nginx closes the way in, not the kernel bug.
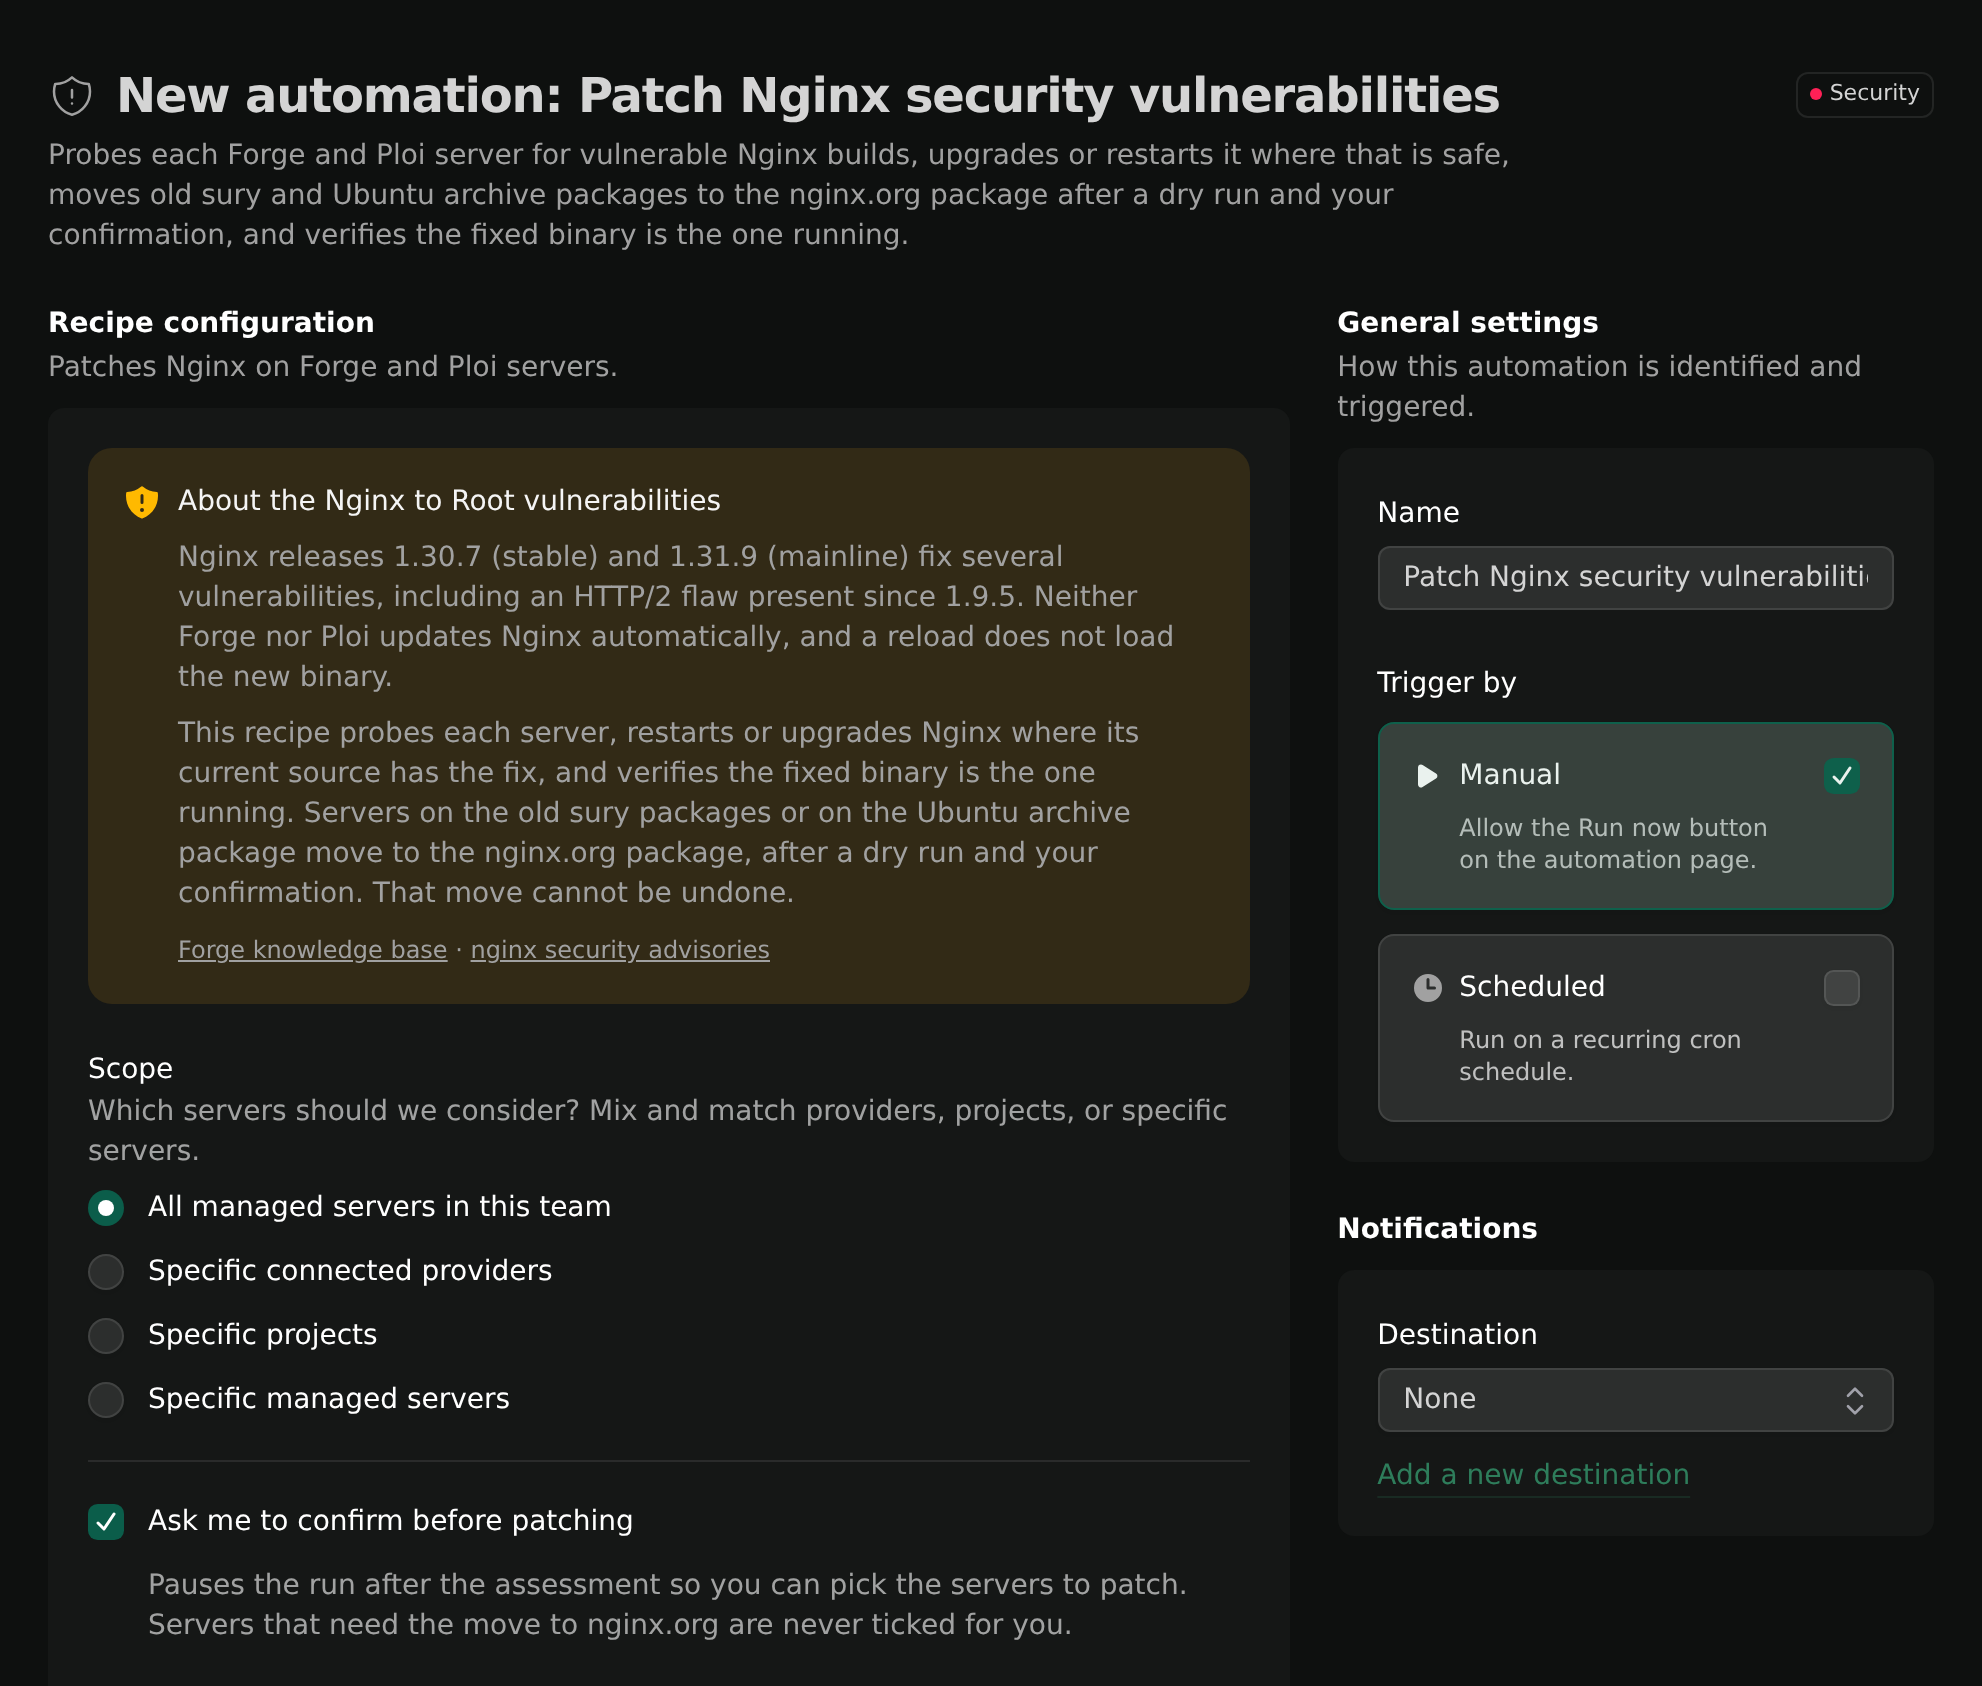
Neither Forge nor Ploi upgrades nginx for you, so I prepared an automation in Unolia. It checks every Forge and Ploi server, upgrades or restarts nginx where that is safe, and confirms the fixed binary is the one running. Servers on the old sury packages or an unpatched Ubuntu package move to the nginx.org package, after a dry run and your go-ahead. Run it once, or schedule it every night so a server added later gets patched too.